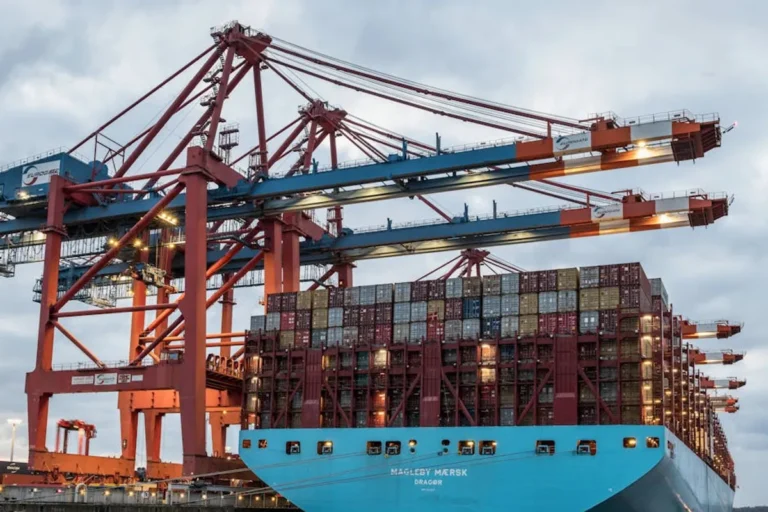
The maritime industry, a cornerstone of global trade and logistics, faces an escalating threat landscape from cyber attacks. As digitalization permeates every aspect of vessel operations, port management, and supply chain logistics, the attack surface expands, making robust cybersecurity not merely a compliance issue but a critical operational imperative. Understanding the evolving trends in maritime cybersecurity is essential for shipowners, operators, port authorities, and logistics providers to allocate resources effectively and implement proactive defense strategies that safeguard assets, ensure business continuity, and protect human life at sea. This emphasizes the need for reliable supply chain security in maritime operations.
Evolving Cyber Threats Targeting Maritime Operations
The nature of cyber threats against the maritime sector is becoming more sophisticated, moving beyond opportunistic attacks to targeted campaigns that leverage advanced techniques. These threats aim to disrupt operations, extort funds, or compromise sensitive data.
Ransomware and Supply Chain Interdiction
Ransomware remains a primary concern, with attacks increasingly targeting operational technology (OT) systems in addition to traditional IT networks. The commercial impact extends beyond immediate financial demands, encompassing significant operational downtime, cargo delays, and reputational damage. Supply chain attacks leverage trusted relationships, compromising software vendors or service providers to gain access to maritime organizations' systems. A single breach in a critical supplier can cascade through the entire maritime ecosystem, affecting numerous vessels, ports, and logistics firms.
- Operational Disruption: Attacks can disable navigation systems, cargo handling equipment, and communication channels.
- Financial Extortion: Direct ransom payments, recovery costs, and legal fees.
- Reputational Damage: Loss of trust from clients and partners due to service interruptions or data breaches.
- Interdiction: The ability for attackers to halt or reroute shipments, impacting global trade flows.
OT/IT Convergence Vulnerabilities
The integration of operational technology (OT) systems—which control physical processes like propulsion, navigation, and cargo handling—with information technology (IT) networks is a growing vulnerability. While convergence offers efficiency gains, it also exposes previously isolated OT environments to internet-borne threats. Legacy OT systems often lack modern security features, making them particularly susceptible to exploitation once a bridge from the IT network is established. This creates critical entry points for attackers to manipulate vessel controls or port infrastructure.
Satellite Communication (SatCom) System Exploits
Satellite communication is vital for maritime operations, enabling navigation, weather updates, crew welfare, and remote monitoring. However, vulnerabilities in SatCom hardware, software, or ground infrastructure present a significant risk. Exploiting these systems can lead to GPS spoofing, jamming of critical communications, or unauthorized access to vessel networks. The potential for misdirection, data interception, or complete communication blackouts poses direct safety and security threats to vessels and their crews.
Insider Threats and the Human Element
Despite technological advancements, the human element remains a critical vulnerability. Insider threats, whether malicious or accidental, can bypass even the most robust technical controls. Phishing, social engineering, and the use of compromised credentials continue to be effective attack vectors. Crew members, port staff, and shore-based personnel with access to sensitive systems or data can inadvertently introduce malware or become unwitting accomplices in cyber attacks. Adequate training and a strong security culture are essential to mitigate these risks.
Regulatory Pressure and Compliance Evolution
International and national regulatory bodies are increasing pressure on the maritime sector to enhance cybersecurity posture. Organizations like the IMO (International Maritime Organization) have issued guidelines, and flag states are implementing stricter requirements. Non-compliance can result in significant penalties, operational restrictions, and insurance complications. Staying abreast of evolving mandates, such as those from the IMO 2021 resolution on cyber risk management, is crucial for maintaining operational licenses and market access. Compliance is also reflected in modern maritime insurance practices and their implications.
AI/ML in Threat Detection and Attack Automation
Artificial intelligence and machine learning are double-edged swords in cybersecurity. While these technologies are increasingly deployed to enhance threat detection, anomaly identification, and automate security responses, attackers are also leveraging AI/ML to develop more sophisticated and evasive malware, automate phishing campaigns, and accelerate vulnerability exploitation. This creates an arms race where maritime organizations must invest in AI-driven defenses to counter AI-powered threats.
Pro Tip: Proactive threat hunting and continuous vulnerability management are more effective than reactive incident response. Implement a dedicated security operations center (SOC) or partner with a specialized managed security service provider (MSSP) that understands maritime OT environments. Regular penetration testing, focusing on both IT and OT systems, identifies weaknesses before attackers exploit them.
Strategic Preparedness for Maritime Cybersecurity
Addressing these trends requires a multi-faceted approach that integrates technology, process, and people.
Implementing Layered Security Architectures
A defense-in-depth strategy is paramount. This involves deploying multiple security controls across different layers of the IT and OT infrastructure, including firewalls, intrusion detection/prevention systems, endpoint protection, and network segmentation. Isolating critical OT systems from general IT networks and implementing strict access controls can significantly reduce the attack surface.
Robust Incident Response Planning
Developing and regularly testing a comprehensive incident response plan is non-negotiable. This plan should outline clear procedures for detection, containment, eradication, recovery, and post-incident analysis. It must include communication protocols for internal stakeholders, regulatory bodies, and external partners, ensuring a swift and coordinated response to minimize damage and accelerate recovery.
Continuous Crew Training and Awareness
Regular cybersecurity training for all crew members and shore-based staff is fundamental. Training should cover phishing recognition, secure browsing habits, password hygiene, and reporting suspicious activities. Simulating real-world attack scenarios can help personnel understand their role in the overall security posture and react appropriately during an actual incident.
Collaboration and Threat Intelligence Sharing
The maritime industry benefits from collective defense. Participating in industry-specific information sharing and analysis centers (ISACs) or other threat intelligence platforms allows organizations to receive timely alerts on emerging threats and share best practices. This collaborative approach strengthens the entire sector's resilience against common adversaries.
Moving Forward: A Proactive Stance
The maritime sector's reliance on digital systems will only grow, making cybersecurity an ongoing, dynamic challenge. Organizations that prioritize cybersecurity as a strategic investment, rather than a mere IT overhead, will be better positioned to navigate the complex threat landscape. This means fostering a security-conscious culture from the bridge to the boardroom, continuously assessing risks, and adapting security measures to counter evolving threats. Proactive planning, robust technological safeguards, and well-trained personnel are the pillars of resilience in an increasingly interconnected and threatened maritime world.
Frequently Asked Questions
What is the biggest cybersecurity threat to the maritime industry this year?
Ransomware and supply chain attacks targeting both IT and OT systems represent the most significant immediate threat, capable of causing widespread operational disruption and substantial financial losses across the maritime ecosystem.
How can vessels protect their operational technology (OT) systems from cyber attacks?
Protecting OT systems involves segmenting them from IT networks, implementing strict access controls, regularly patching software where possible, conducting vulnerability assessments specific to OT, and ensuring physical security of control systems.
What role does crew training play in maritime cybersecurity?
Crew training is critical as human error is a common attack vector. Educating personnel on phishing, social engineering, secure practices, and incident reporting protocols forms a crucial line of defense against cyber threats.
Are international regulations for maritime cybersecurity becoming stricter?
Yes, international bodies like the IMO are continually updating guidelines and resolutions, such as the IMO 2021 requirements, pushing for more comprehensive cyber risk management. Flag states and port authorities are increasingly enforcing these stricter compliance standards.