Ecommerce brands operating within or relying on global supply chains face a distinct set of cybersecurity challenges, particularly those involving maritime logistics. While internal network security and customer data protection remain paramount, the vulnerabilities extend far beyond a brand's direct digital infrastructure. The interconnected nature of modern shipping means that a cyber incident at any point – from a port terminal's operational technology (OT) systems to a shipping line's booking platform – can halt cargo, expose sensitive information, or disrupt delivery schedules, directly impacting revenue and customer trust. Understanding these specific risks and the common missteps is crucial for maintaining supply chain integrity and safeguarding commercial operations. For ecommerce brands looking to bolster their defenses, consulting a comprehensive maritime cybersecurity checklist can highlight overlooked areas.
Overlooking Supply Chain Cyber Resilience
A significant mistake ecommerce brands make is assuming their cybersecurity responsibilities end at their own enterprise perimeter. Modern supply chains are complex, involving multiple third-party logistics providers (3PLs), freight forwarders, port authorities, and customs agencies. Each entity represents a potential point of failure. Brands often fail to extend their security posture or due diligence to these external partners, creating blind spots that adversaries exploit.
- Lack of Third-Party Security Audits: Many brands do not regularly audit the cybersecurity practices of their shipping partners. This includes evaluating their incident response plans, data encryption protocols, and employee training programs. Without this oversight, a brand effectively outsources its risk without understanding the exposure.
- Insufficient Contractual Safeguards: Supply chain contracts frequently prioritize cost and delivery times over explicit cybersecurity clauses. Agreements should specify minimum security standards, notification requirements for breaches, and liability frameworks related to cyber incidents.
- Ignoring Nth-Party Risks: A shipping line might have robust security, but what about its cloud provider, its port terminal operator, or the software vendor for its vessel management system? The chain of trust extends far beyond direct partners, and a breach at an Nth-party can cascade.
Neglecting Operational Technology (OT) Vulnerabilities
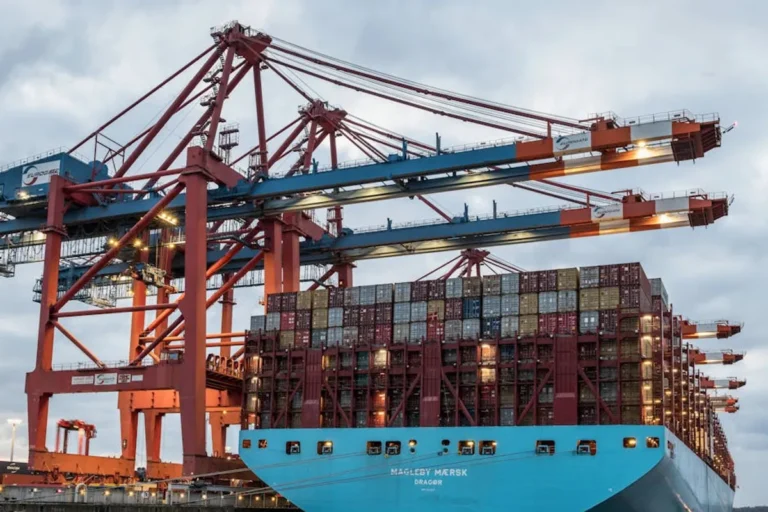
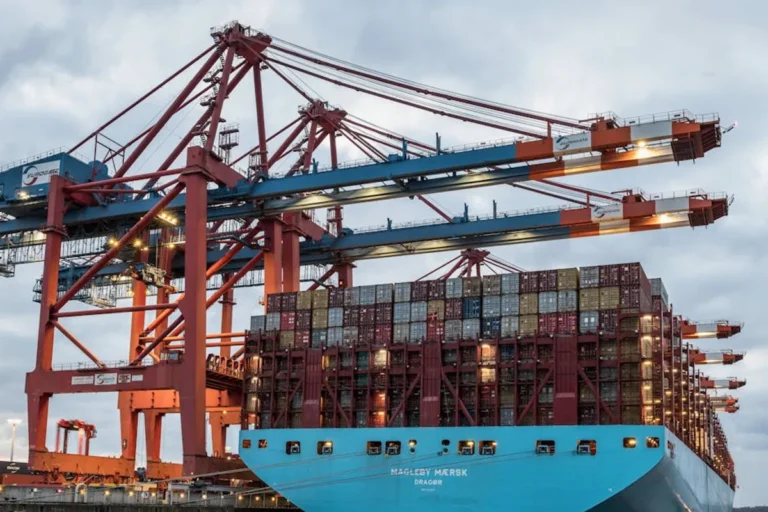
While most ecommerce brands focus on IT security (laptops, servers, websites), maritime logistics heavily relies on Operational Technology (OT). This includes systems controlling cranes, vessel navigation, cargo handling, and port access. OT environments often have different vulnerabilities than traditional IT networks:
Common OT Security Gaps:
- Legacy Systems: Many OT systems are older, running outdated software, making them difficult to patch and inherently more vulnerable to modern attacks.
- Network Convergence: The increasing integration of IT and OT networks for efficiency creates new pathways for attackers to move from an IT breach into critical operational systems.
- Remote Access Risks: Remote maintenance and monitoring of OT systems, while convenient, can introduce insecure access points if not rigorously secured with multi-factor authentication and strict access controls.
A successful attack on port OT, for instance, could shut down cargo operations, leading to massive delays and financial losses for any ecommerce brand relying on that port for imports or exports.
Inadequate Data Protection for Cargo and Customer Information
Shipping manifests, customs declarations, customer delivery addresses, and payment details are routinely transmitted across various entities in the maritime supply chain. A common mistake is failing to apply consistent, end-to-end data protection measures.
Specific Data Protection Errors:
- Unencrypted Communications: Information exchanged via email, EDI (Electronic Data Interchange), or other systems without strong encryption can be intercepted. This exposes not only cargo details but also potentially sensitive customer data.
- Poor Access Management: Too many individuals or systems within the supply chain might have access to sensitive data without a clear "need-to-know" basis. This expands the attack surface.
- Lack of Data Minimization: Brands often share more data than strictly necessary. For example, a freight forwarder may not need full customer payment details, only shipping information. Over-sharing increases risk.
Pro Tip: Implement a data classification policy for all information shared with maritime partners. Mandate encryption for all data in transit and at rest, especially for personally identifiable information (PII) and commercially sensitive cargo details. Regularly review access logs for anomalies.
Underestimating Phishing and Social Engineering Attacks
Cybercriminals frequently target employees involved in logistics, finance, and customs with highly sophisticated phishing and social engineering tactics. These attacks aim to trick staff into revealing credentials, transferring funds to fraudulent accounts, or rerouting shipments.
Examples of Targeted Attacks:
- Business Email Compromise (BEC): Impersonating a shipping partner or internal executive to request fraudulent payments for shipping invoices or to alter delivery instructions.
- Credential Harvesting: Phishing emails designed to steal login credentials for logistics portals, customs systems, or internal enterprise resource planning (ERP) systems.
- Cargo Diversion Scams: Using social engineering to trick logistics personnel into changing delivery destinations, leading to theft of goods.
Ecommerce brands must provide robust, ongoing cybersecurity training specifically tailored to these types of threats for all employees interacting with the supply chain.
Absence of a Maritime-Specific Incident Response Plan
Many ecommerce brands have general incident response plans, but these often lack specific protocols for maritime cyber incidents. A breach affecting a port, a vessel, or a logistics partner requires a different response than an internal IT system compromise.
Key Omissions in Planning:
- Lack of Communication Protocols: How will the brand communicate with affected shipping partners, customers, and regulatory bodies during a maritime cyber event? Who is responsible for what?
- Supply Chain Contingency: What are the alternative shipping routes or logistics providers if a primary port or carrier is compromised? This needs to be pre-planned and tested.
- Legal and Regulatory Compliance: Maritime incidents can trigger specific international regulations (e.g., IMO 2021 guidelines for vessel cybersecurity, various port security mandates). Response plans must account for these.
Strengthening Your Maritime Cyber Defenses
Ecommerce brands must proactively address these vulnerabilities. This involves extending cybersecurity governance beyond internal IT, engaging deeply with supply chain partners, and preparing for specific maritime-related threats. Prioritizing vendor risk management, securing operational technologies, and developing tailored incident response plans are not just best practices, but essential components of modern commercial resilience.
Frequently Asked Questions
Why is maritime cybersecurity a direct concern for ecommerce brands?
Ecommerce brands rely on global shipping for product sourcing and delivery. A cyberattack on any part of the maritime supply chain – vessels, ports, or logistics providers – can disrupt operations, cause significant delays, compromise cargo, and expose sensitive customer or business data, directly impacting revenue and reputation.
What kind of data is most at risk in maritime cyber incidents?
Key data at risk includes shipping manifests, customs declarations, bill of lading information, customer delivery addresses, payment details, and proprietary product information. Exposure of this data can lead to financial fraud, cargo theft, competitive intelligence loss, and regulatory fines.
Who is ultimately responsible for cybersecurity when multiple parties are involved in a maritime shipment?
While each entity in the supply chain holds responsibility for its own systems, the ecommerce brand initiating or receiving the shipment bears ultimate commercial and reputational risk. Proactive due diligence, contractual agreements, and shared visibility are essential to distribute and manage this responsibility effectively.
What is the first step an ecommerce brand should take to improve maritime cybersecurity?
Begin with a comprehensive risk assessment of your entire supply chain, identifying all third-party logistics providers and their cybersecurity postures. Prioritize partners handling sensitive data or critical operational functions, and establish clear security requirements and audit processes.