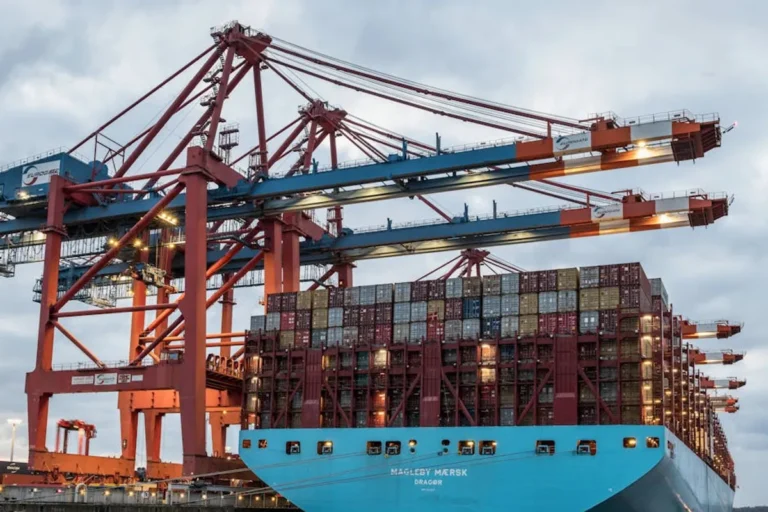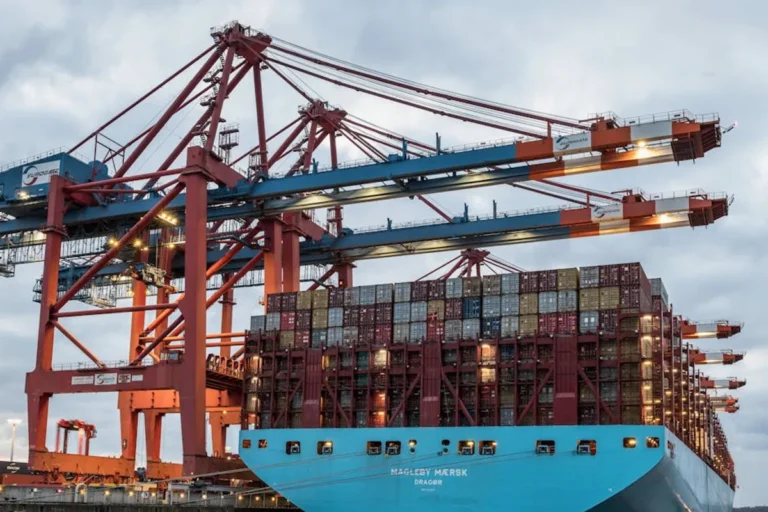
Freight teams operating in the maritime sector face a unique intersection of physical and digital risks. While the movement of goods relies on robust logistics and operational technology, the increasing digitalization of vessels, ports, and supply chain management systems introduces significant cybersecurity vulnerabilities. Understanding and mitigating these threats is no longer an optional add-on but a fundamental requirement for maintaining operational continuity, protecting sensitive data, and ensuring compliance.
Defining Maritime Cybersecurity for Freight Operations
Maritime cybersecurity encompasses the measures and practices designed to protect maritime operational technology (OT) and information technology (IT) systems from cyber threats. This includes everything from shipboard navigation and propulsion systems to port logistics platforms, cargo tracking software, and the broader digital infrastructure supporting global trade. For freight teams, this means safeguarding the digital assets that enable efficient, secure, and compliant movement of goods across oceans and through ports. This underscores the need for reliable supply chain security in maritime operations.
Unlike traditional IT security, maritime cybersecurity must account for the unique operating environment of vessels and ports. Systems are often isolated, legacy hardware is common, satellite communication links present specific vulnerabilities, and the physical security of equipment directly impacts its digital resilience. The convergence of IT systems (e.g., administrative networks, crew welfare systems) with OT systems (e.g., Engine Room Monitoring Systems, Electronic Chart Display and Information Systems – ECDIS) creates complex attack surfaces that require specialized protection strategies.
Critical Vulnerabilities Facing Freight Teams
The interconnected nature of modern logistics exposes freight operations to a range of sophisticated cyber threats. These vulnerabilities can lead to severe disruptions, financial losses, and reputational damage. Key areas of concern include:
- Operational Technology (OT) Compromise: Attacks targeting critical ship systems like navigation, propulsion, or cargo handling can lead to physical damage, grounding, or rerouting of vessels. Such incidents directly threaten crew safety and cargo integrity.
- Supply Chain Attacks: A breach in any link of the complex maritime supply chain – from port operators and logistics providers to software vendors and customs agencies – can compromise data or operations for freight teams further down the line. Trust relationships between entities are often exploited.
- Data Breaches and Ransomware: Sensitive commercial data, cargo manifests, client information, and financial records are prime targets. Ransomware attacks can encrypt critical systems, halting operations until a ransom is paid, often with no guarantee of data recovery.
- Phishing and Social Engineering: Crew members and shoreside personnel are frequently targeted with deceptive emails or messages designed to steal credentials or implant malware. Human error remains a significant entry point for attackers.
- Port Infrastructure Attacks: Cyberattacks on port management systems can disrupt cargo flow, create bottlenecks, and impact the timely loading and unloading of vessels, directly affecting freight schedules and costs.
Developing a Practical Cybersecurity Framework
Implementing an effective maritime cybersecurity strategy requires a structured approach that integrates technology, policy, and human factors. Freight teams should focus on these foundational elements:
Risk Assessment and Asset Identification
Begin by identifying all critical digital assets, both on vessels and shoreside, that support freight operations. This includes navigation systems, cargo management software, communication platforms, and administrative networks. Conduct a thorough risk assessment to understand potential threats, vulnerabilities, and the likely impact of a successful attack on each asset. Prioritize risks based on severity and likelihood.
Technical Safeguards and Controls
Robust technical measures form the backbone of defense. These include:
- Network Segmentation: Isolate OT networks from IT networks to prevent lateral movement of threats. Use firewalls and intrusion detection systems to monitor and control traffic between segments.
- Endpoint Protection: Deploy antivirus and anti-malware solutions on all endpoints, including shipboard computers, servers, and mobile devices. Ensure regular updates and centralized management.
- Vulnerability Management: Establish a routine for identifying and patching software and hardware vulnerabilities across all systems. This includes operating systems, applications, and firmware for OT devices.
- Secure Remote Access: Implement multi-factor authentication (MFA) and virtual private networks (VPNs) for all remote access to shipboard or shoreside systems. Monitor remote connections for unusual activity.
- Data Backup and Recovery: Regularly back up critical data, storing copies both on-site and off-site. Develop and test a comprehensive disaster recovery plan to ensure business continuity after an incident.
Pro Tip: Focus on the "crown jewels" of your operation first. Identify the systems whose compromise would cause the most significant operational disruption or financial loss and prioritize their protection. This ensures resources are allocated where they deliver the highest impact.
Operational Policies and Crew Training
Technology alone is insufficient. Human elements and clear policies are equally vital:
- Cybersecurity Policies: Develop clear, enforceable policies for password management, acceptable use of IT/OT systems, data handling, and incident reporting. Ensure these policies are regularly reviewed and updated.
- Crew and Staff Training: Conduct regular cybersecurity awareness training for all crew members and shoreside personnel. This should cover phishing recognition, secure browsing habits, proper use of removable media, and incident reporting procedures. Tailor training to specific roles and responsibilities.
- Incident Response Plan: Create a detailed incident response plan that outlines steps to take before, during, and after a cyberattack. This includes communication protocols, forensic investigation procedures, and recovery steps. Test the plan periodically through drills and simulations.
Regulatory Compliance and Standards
The maritime industry is increasingly regulated regarding cybersecurity. Freight teams must ensure compliance with relevant international and national standards. The International Maritime Organization (IMO) Resolution MSC.428(98) mandates that cyber risk management is addressed in safety management systems by January 1, 2021. Adherence to frameworks like NIST Cybersecurity Framework or ISO/IEC 27001 can provide a structured approach to meeting these obligations and demonstrating due diligence.
Implementing and Maintaining Your Strategy
Building a robust maritime cybersecurity posture is an ongoing process, not a one-time project. For freight teams, this means integrating security into daily operations and continuously adapting to the evolving threat landscape. Regular audits, penetration testing, and vulnerability scanning are essential to identify weaknesses before attackers do. Foster a culture of security awareness across all levels of the organization, from the bridge to the back office, recognizing that every individual plays a role in collective defense.
Frequently Asked Questions
What is the primary difference between IT and OT cybersecurity in maritime?
IT cybersecurity focuses on protecting data confidentiality, integrity, and availability in administrative systems, while OT cybersecurity prioritizes the safety, reliability, and availability of physical operational systems (e.g., navigation, propulsion) where a breach could have physical consequences.
Why is crew training so important for maritime cybersecurity?
Crew members are often the first line of defense and the most common target for social engineering attacks like phishing. Well-trained personnel can identify and report suspicious activities, preventing breaches that bypass technical controls.
What is the IMO 2021 cybersecurity regulation?
The IMO Resolution MSC.428(98) requires that maritime cyber risk management be incorporated into a vessel's safety management system by the first annual verification of the Document of Compliance after January 1, 2021. It mandates a systematic approach to identifying, assessing, and mitigating cyber risks.