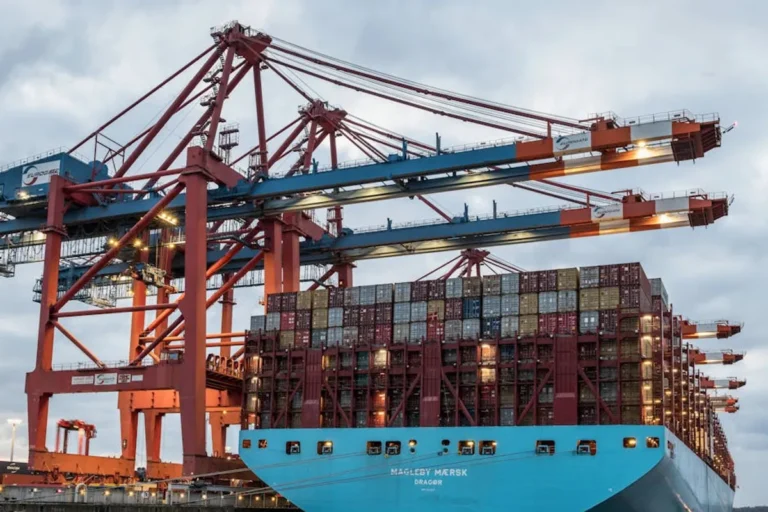
Maritime cybersecurity addresses the specific threats and vulnerabilities inherent in the shipping and offshore industries. For B2B companies operating within or supporting this sector, understanding and implementing robust maritime cybersecurity measures is not merely a compliance issue; it is a critical operational imperative. The convergence of operational technology (OT) and information technology (IT) systems on vessels, ports, and logistics networks creates unique attack surfaces that demand specialized protection. Neglecting these digital defenses can lead to severe financial losses, operational disruptions, environmental incidents, and reputational damage.
Understanding the Maritime Threat Landscape
The maritime sector presents a distinct set of cybersecurity challenges, differing significantly from typical enterprise IT environments. These differences stem from the global, interconnected, and often remote nature of maritime operations.
Unique Vulnerabilities of Maritime Operations
Maritime systems are characterized by several inherent vulnerabilities that cyber attackers exploit:
- Satellite Communication Dependence: Vessels rely heavily on satellite links for navigation, communication, and data transfer, which can be susceptible to interception, jamming, or spoofing.
- OT/IT Convergence: The integration of operational systems (e.g., engine controls, navigation, cargo management) with standard IT networks creates pathways for cyber threats to impact physical operations.
- Remote and Distributed Assets: Ships operate globally, often with limited direct IT support, making patching, monitoring, and incident response more complex.
- Supply Chain Dependencies: The maritime supply chain involves numerous third-party vendors, port authorities, and logistics partners, each representing a potential entry point for attacks.
- Legacy Systems: Many vessels and port infrastructures utilize older, proprietary systems that lack modern security features and are difficult to update.
Common Attack Vectors
Attackers leverage various methods to compromise maritime systems, often targeting the weakest links:
- Phishing and Spear-Phishing: Targeting crew members or shore-based personnel with deceptive emails to gain access to credentials or deploy malware.
- Ransomware: Encrypting critical operational data or systems, demanding payment for their release. This can cripple port operations or vessel movements.
- Malware and Viruses: Infiltrating systems through infected USB drives, compromised downloads, or network vulnerabilities, leading to data theft or system disruption.
- GPS Spoofing and AIS Manipulation: Deceiving navigation systems or falsely reporting vessel positions, potentially leading to collision, grounding, or misdirection for illicit activities.
- Port System Breaches: Attacking the IT and OT systems of port facilities, impacting cargo handling, customs, and logistics.
Key Pillars of a Maritime Cybersecurity Strategy
A robust maritime cybersecurity strategy for B2B companies must integrate several foundational elements to address the sector's unique risks effectively.
Risk Assessment and Governance
Implementing effective cybersecurity begins with a thorough understanding of an organization's specific risk profile. This involves identifying critical assets, assessing potential threats, and evaluating existing controls. Compliance with international regulations, such as the IMO 2021 guidelines, is mandatory for many maritime operators, requiring cyber risk management to be incorporated into safety management systems. Establishing clear policies, roles, and responsibilities for cybersecurity across the organization is also crucial for effective governance.
Technology Implementation
Strategic technology deployment forms the backbone of defense:
- Network Segmentation: Isolating critical OT networks from less secure IT networks to prevent lateral movement of threats.
- Endpoint Protection: Deploying advanced antivirus, anti-malware, and intrusion detection systems on all connected devices, both ashore and afloat.
- Secure Satellite Communication: Implementing encryption, secure VPNs, and robust authentication for all satellite-based data transfers.
- Vulnerability Management: Regularly scanning systems for vulnerabilities and applying patches promptly.
- Data Backup and Recovery: Establishing offsite, immutable backups and comprehensive recovery plans to mitigate ransomware impacts.
Human Element and Training
People are often the first line of defense and, conversely, the most common point of failure. Regular, tailored training for all personnel—from senior management to crew members—is essential. This includes awareness campaigns on phishing, social engineering, and safe internet practices. Incident response drills help teams practice their roles in a cyber-attack scenario, improving reaction times and minimizing damage.
Supply Chain Security
Given the interconnectedness of the maritime ecosystem, securing the supply chain is paramount. This involves rigorous vetting of all third-party vendors, suppliers, and partners for their cybersecurity posture. Contracts should include clear cybersecurity clauses, requiring adherence to specific standards and prompt notification of breaches. Continuous monitoring of third-party risks helps manage this extended attack surface.
Implementing a Robust Maritime Cybersecurity Program
For B2B companies, a structured approach to implementing cybersecurity measures ensures comprehensive coverage and minimizes operational disruption.
Initial Steps for B2B Companies
Best for: Establishing foundational security and compliance.
- Conduct a Comprehensive Cyber Risk Audit: Identify all IT and OT assets, assess their criticality, and pinpoint vulnerabilities and potential threat vectors specific to your maritime operations.
- Develop an Incident Response Plan (IRP): Create a clear, actionable plan outlining steps to detect, contain, eradicate, and recover from a cyber incident. This plan should be tested regularly.
- Invest in Specialized Training: Provide ongoing cybersecurity awareness training for all employees, emphasizing maritime-specific threats and best practices.
- Establish Clear Communication Protocols: Define how cyber incidents will be reported, escalated, and communicated internally and externally to relevant authorities or partners.
- Implement Multi-Factor Authentication (MFA): Mandate MFA for all remote access, critical systems, and sensitive data access points.
Pro Tip: Beyond technical controls, cultivate a strong cybersecurity culture. Regular, engaging training sessions and clear internal communication about evolving threats are often more effective than relying solely on software. Employees, especially those working remotely or on vessels, must understand their role in the overall security posture.
Navigating Regulatory Compliance and Standards
Compliance is a significant driver for maritime cybersecurity, with international bodies and national governments introducing mandatory requirements.
IMO 2021 Guidelines
The International Maritime Organization (IMO) made cyber risk management mandatory for all ships under its Safety Management System (SMS) from January 1, 2021. This requires companies to identify cyber risks, implement safeguards, and ensure they are part of the ship's safety management. Compliance is essential for vessel certification and avoiding port state control detentions.
Other Relevant Frameworks
While IMO 2021 is specific to maritime, broader cybersecurity frameworks also apply:
- NIST Cybersecurity Framework: Provides a comprehensive set of guidelines for identifying, protecting, detecting, responding to, and recovering from cyber threats.
- ISO 27001: An international standard for information security management systems, offering a systematic approach to managing sensitive company information.
- NIS2 Directive (EU): Expands cybersecurity requirements for critical entities, potentially impacting maritime B2B companies operating within the EU or serving EU clients.
Securing Your Maritime Operations: A Strategic Imperative
For B2B companies engaged in the maritime sector, proactive cybersecurity is no longer optional. The interconnectedness of modern shipping, the increasing sophistication of cyber threats, and the stringent regulatory landscape demand a continuous, adaptive approach. By focusing on risk assessment, robust technology, human training, and supply chain vigilance, companies can build resilience against cyber-attacks, safeguard their operations, and maintain trust within the global maritime ecosystem. Investing in these defenses protects not just data, but the very continuity of business and the safety of maritime assets.
Frequently Asked Questions About Maritime Cybersecurity
Why is maritime cybersecurity different from general IT security?
Maritime cybersecurity faces unique challenges due to the convergence of operational technology (OT) and information technology (IT) on vessels and in ports, reliance on satellite communications, remote operating environments, and a complex global supply chain. These factors create distinct vulnerabilities and attack vectors not typically present in standard enterprise IT setups.
What is the IMO 2021 regulation?
The IMO 2021 regulation refers to the International Maritime Organization's mandate that, as of January 1, 2021, cyber risk management must be incorporated into a ship's Safety Management System (SMS). This requires shipping companies to identify, assess, and manage cyber risks in their operations to ensure safe and secure vessel operations.
How can small B2B maritime companies afford robust cybersecurity?
Small B2B maritime companies can implement robust cybersecurity through layered approaches: starting with essential risk assessments, leveraging cost-effective cloud-based security solutions, prioritizing employee training, and considering managed security services (MSSPs) that specialize in maritime environments to outsource expertise.
What are the immediate risks of neglecting maritime cybersecurity?
Neglecting maritime cybersecurity can lead to immediate risks such as operational disruptions (e.g., port closures, vessel diversions), financial losses from ransomware or data theft, reputational damage, regulatory fines for non-compliance, and even safety or environmental incidents if critical control systems are compromised.